สามารถติดตามข่าวสารได้ที่ webboard หรือ Facebook NCSA Thailand 
Forum wide moderators
สามารถติดตามข่าวสารได้ที่ webboard หรือ Facebook NCSA Thailand
สามารถติดตามข่าวสารได้ที่ webboard หรือ Facebook NCSA Thailand 
สามารถติดตามข่าวสารได้ที่ webboard หรือ Facebook NCSA Thailand 
Industrial Sector
New Tooling
Vulnerabilities
Malware
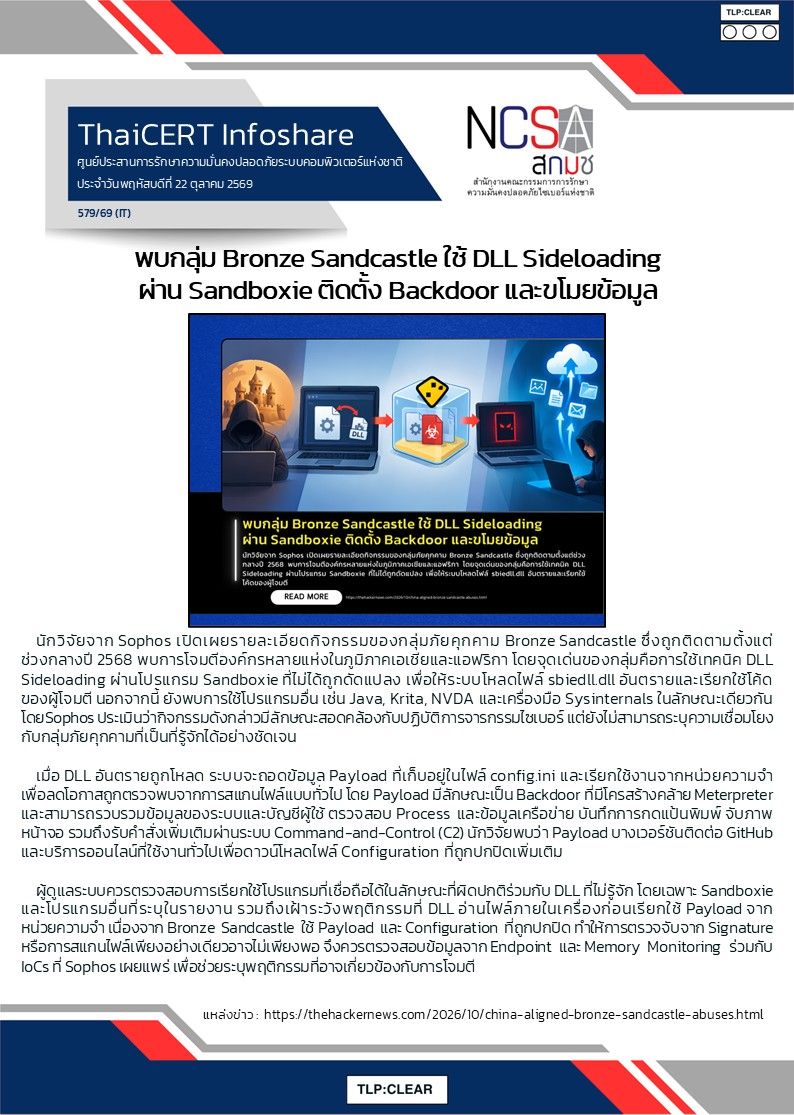
 (CTU) and SophosLabs researchers investigated a cluster of incidents attributed to the BRONZE SANDCASTLE threat group. The most distinctive technical marker for BRONZE SANDCASTLE is its consistent use of Sandboxie DLL sideloading. Across multiple victims’ environments, legitimate Sandboxie executables were placed alongside a malicious sbiedll.dll file, causing the trusted application to load attacker-controlled code at runtime. This consistent pattern functions as a signature for the group, although the threat actors employ several other sideloading file combinations as well (see Table 1)."
Breaches/Hacks/Leaks
General News
อ้างอิง
Electronic Transactions Development Agency (ETDA) 
สามารถติดตามข่าวสารได้ที่ webboard หรือ Facebook NCSA Thailand 
สามารถติดตามข่าวสารได้ที่ webboard หรือ Facebook NCSA Thailand 
สามารถติดตามข่าวสารได้ที่ webboard หรือ Facebook NCSA Thailand 
Industrial Sector
Vulnerabilities
Malware
 software, which could allow unauthorized attackers to circumvent security controls and initiate virtual private network (VPN) connections. This CVE was added to the Known Exploited Vulnerability (KEV) catalog on May 13, 2026."
Breaches/Hacks/Leaks
General News
อ้างอิง
Electronic Transactions Development Agency (ETDA) 
สามารถติดตามข่าวสารได้ที่ webboard หรือ Facebook NCSA Thailand 
สามารถติดตามข่าวสารได้ที่ webboard หรือ Facebook NCSA Thailand